The dashboard: endpoint and credential counts at a glance
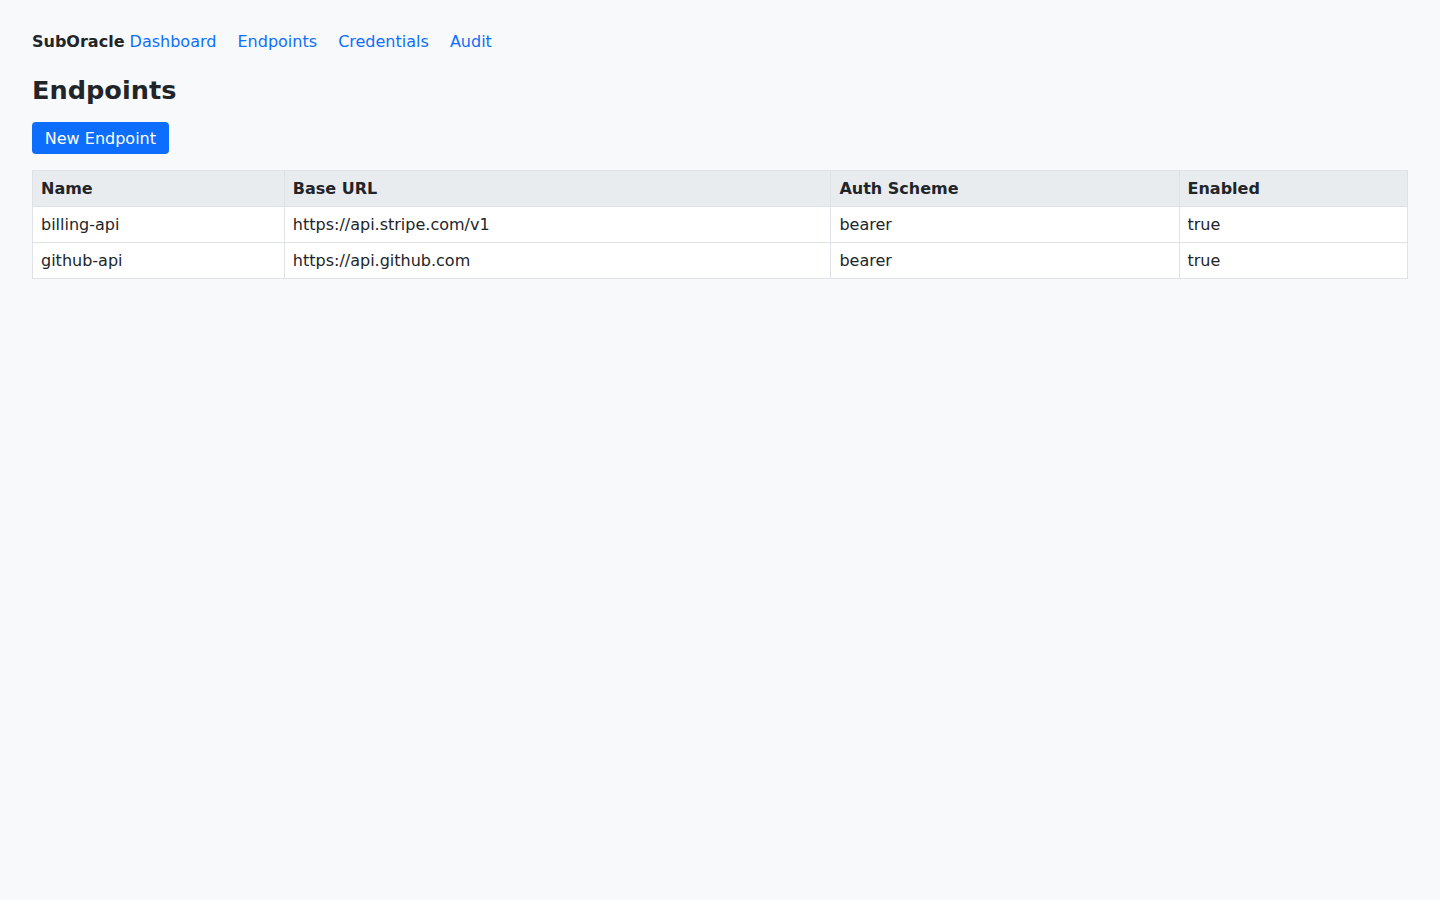
Endpoints: auth scheme, placement and enable state
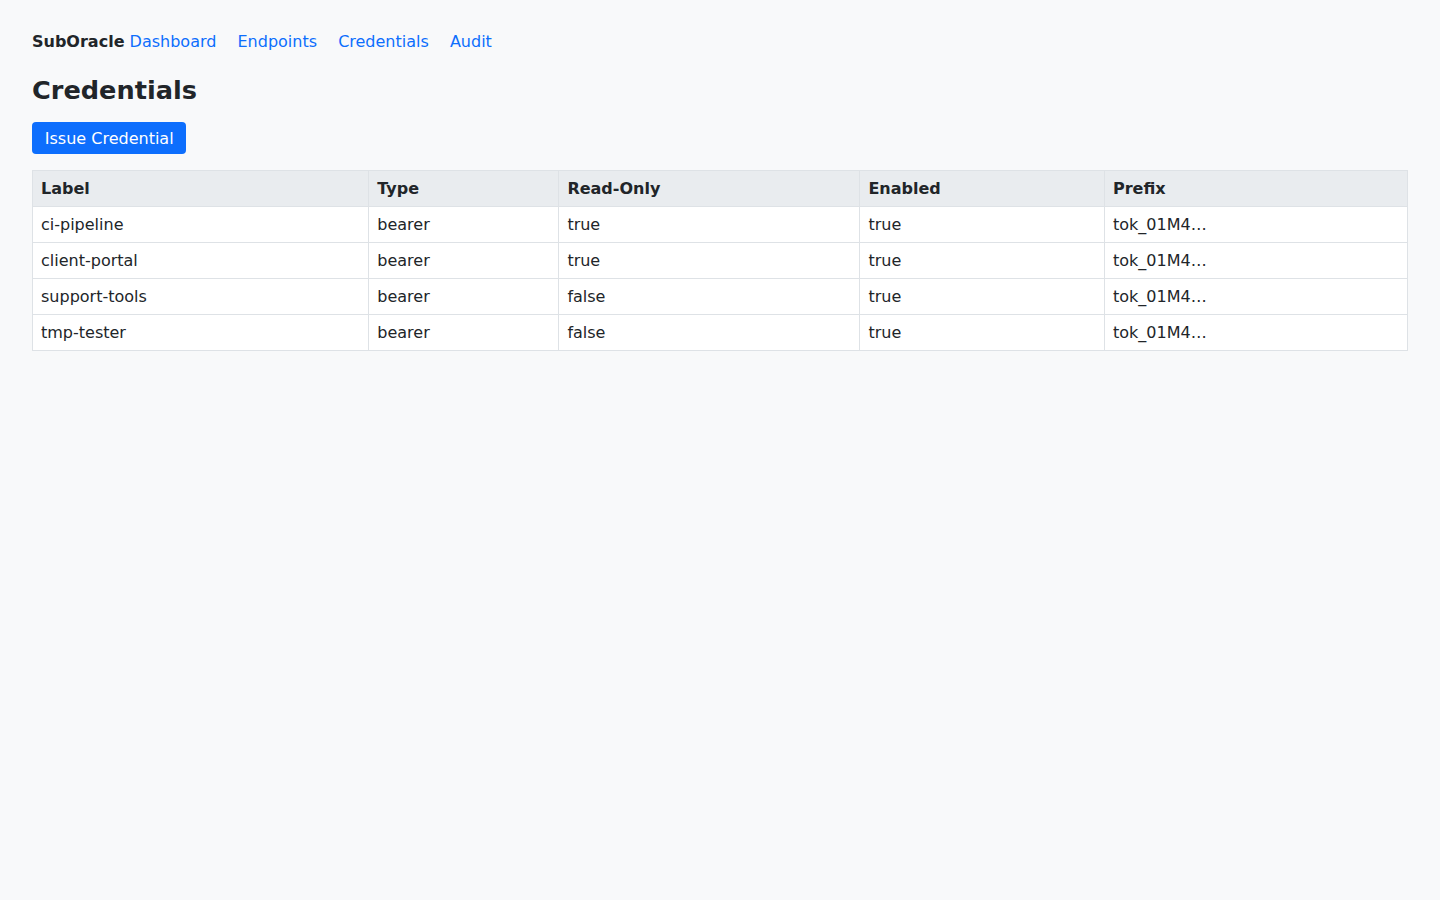
Credentials: scoped, read-only where needed, prefix-only display
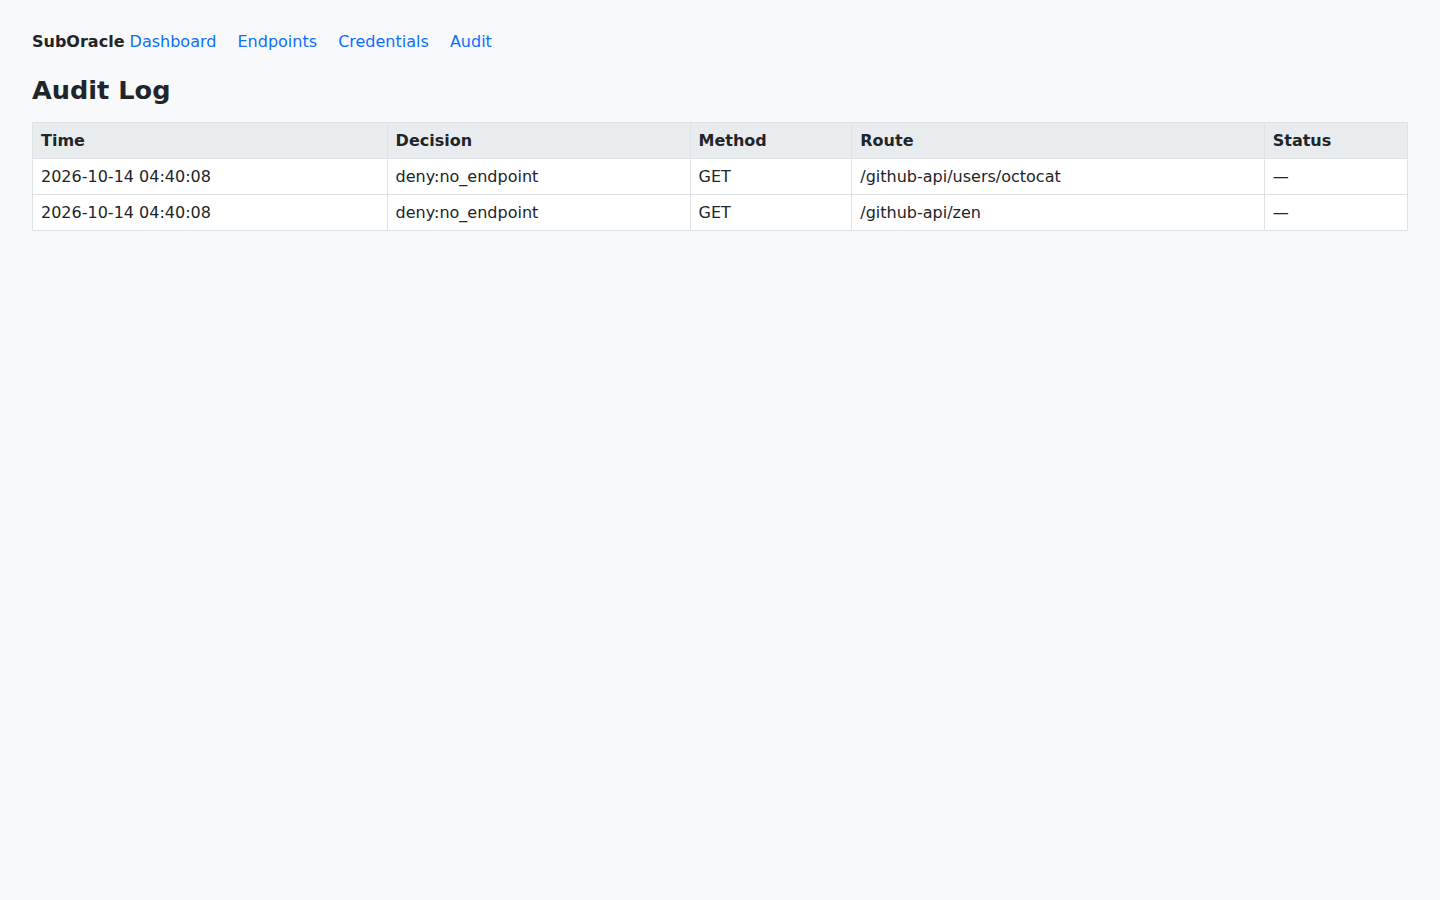
The audit log: every decision the proxy made
SubOracle Built
security proxy for SaaS APIsA security proxy that sits between automation components and the SaaS APIs they touch. Credentials stay scoped and routes stay on the list.
Automation touches dozens of SaaS APIs. Every one of them wants a credential. SubOracle sits in the middle: the automation talks to it, it talks to the API and the credential never leaves the proxy. Scoped credentials, route allowlists and read-only rules get enforced in one place instead of being re-implemented in every script.
It speaks the auth schemes APIs actually use: API keys, bearer tokens, basic, OAuth2, HMAC and AWS SigV4. It ships with an admin UI, OpenAPI import and an audit store so every request through it is a record.
A credential-injecting proxy sits in the hot path of every request. It has to be small, fast and boring. Go made the concurrency easy and the binary self-contained. The design principle was simple: automation should never hold an upstream credential again.