John Sabo
← All work

Fully managed SOAR for MSPs

Lono Security

lonosecurity.com

SOAR for everyone, fully managed: Lono does the integration and automation development an MSP would otherwise hire a SOAR engineer for, runs it, and charges a flat monthly rate for the service.

What it is

Traditional SOAR is priced and sized for large enterprises, and standing one up runs to months of integration work. Lono is the other bet. It is fully managed: Lono does all the development work, the integrations, the automations, the runbooks, and operates the platform as an ongoing service for a flat monthly rate. An MSP gets a working SOAR without hiring anyone or waiting a quarter for onboarding.

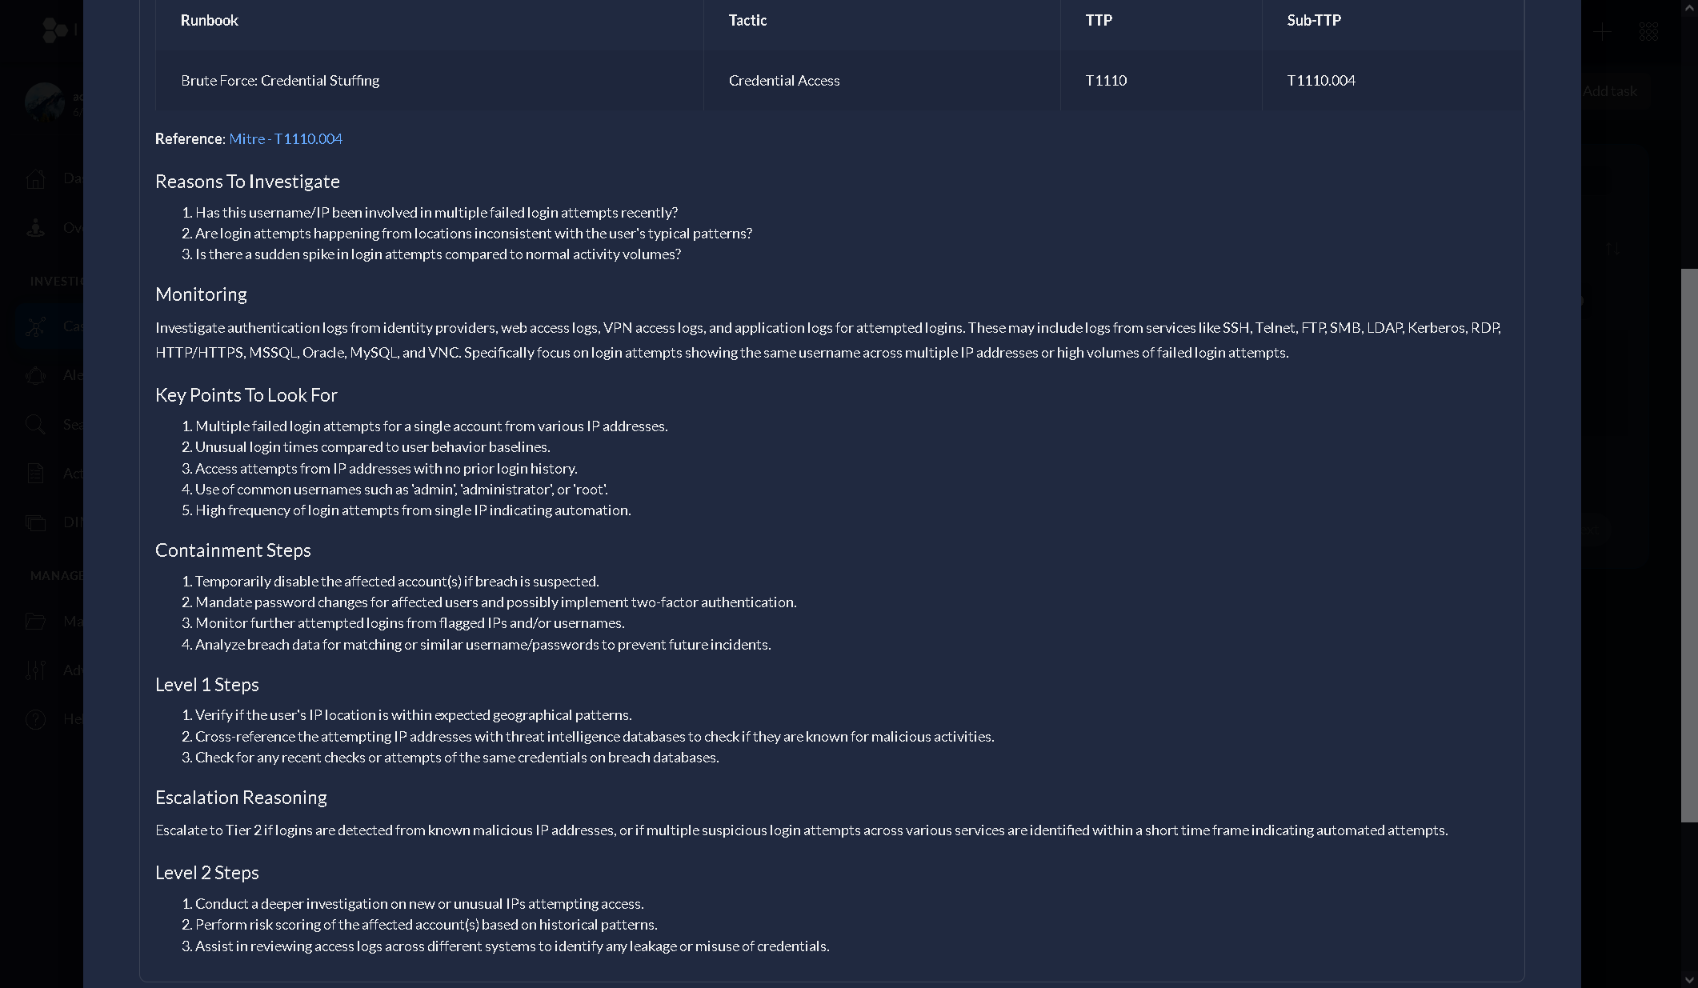
That pricing only works because of how streamlined the platform is. Thirty years of working security data went into the design, so the hard parts arrive already built: ingestion for whatever a client runs, enrichment for every indicator, case management made for cyber and fraud investigations, and a runbook library keyed to MITRE ATT&CK, one per technique and sub-technique. An analyst opens a case and the runbook is already on it: the investigation questions, the containment steps and the escalation path for that exact technique.

The consultancy site carries it: six services, real booking availability, lead capture with nurture email, and the GEO markup that gets the site cited by AI assistants.
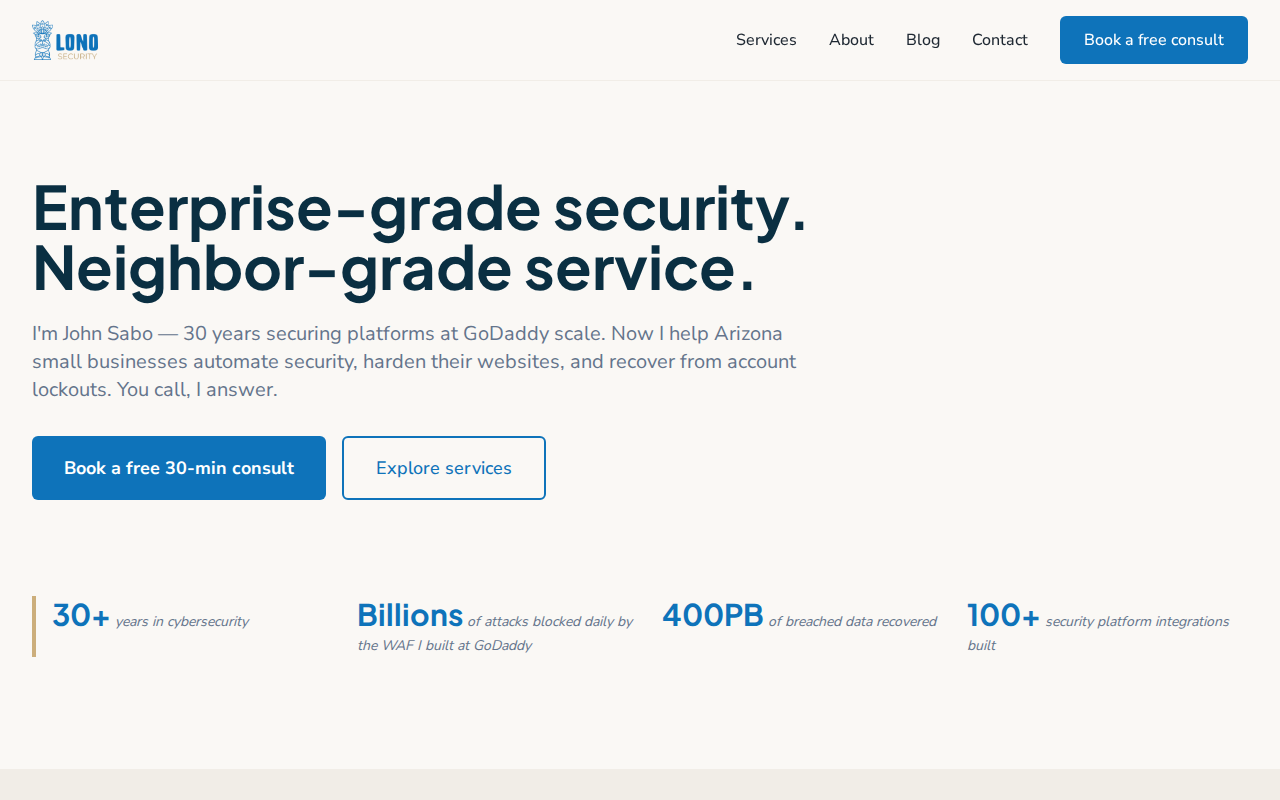
The consultancy site: six services, live booking
The runbook an analyst gets: MITRE T1110.004, written out with Level 1 and Level 2 steps
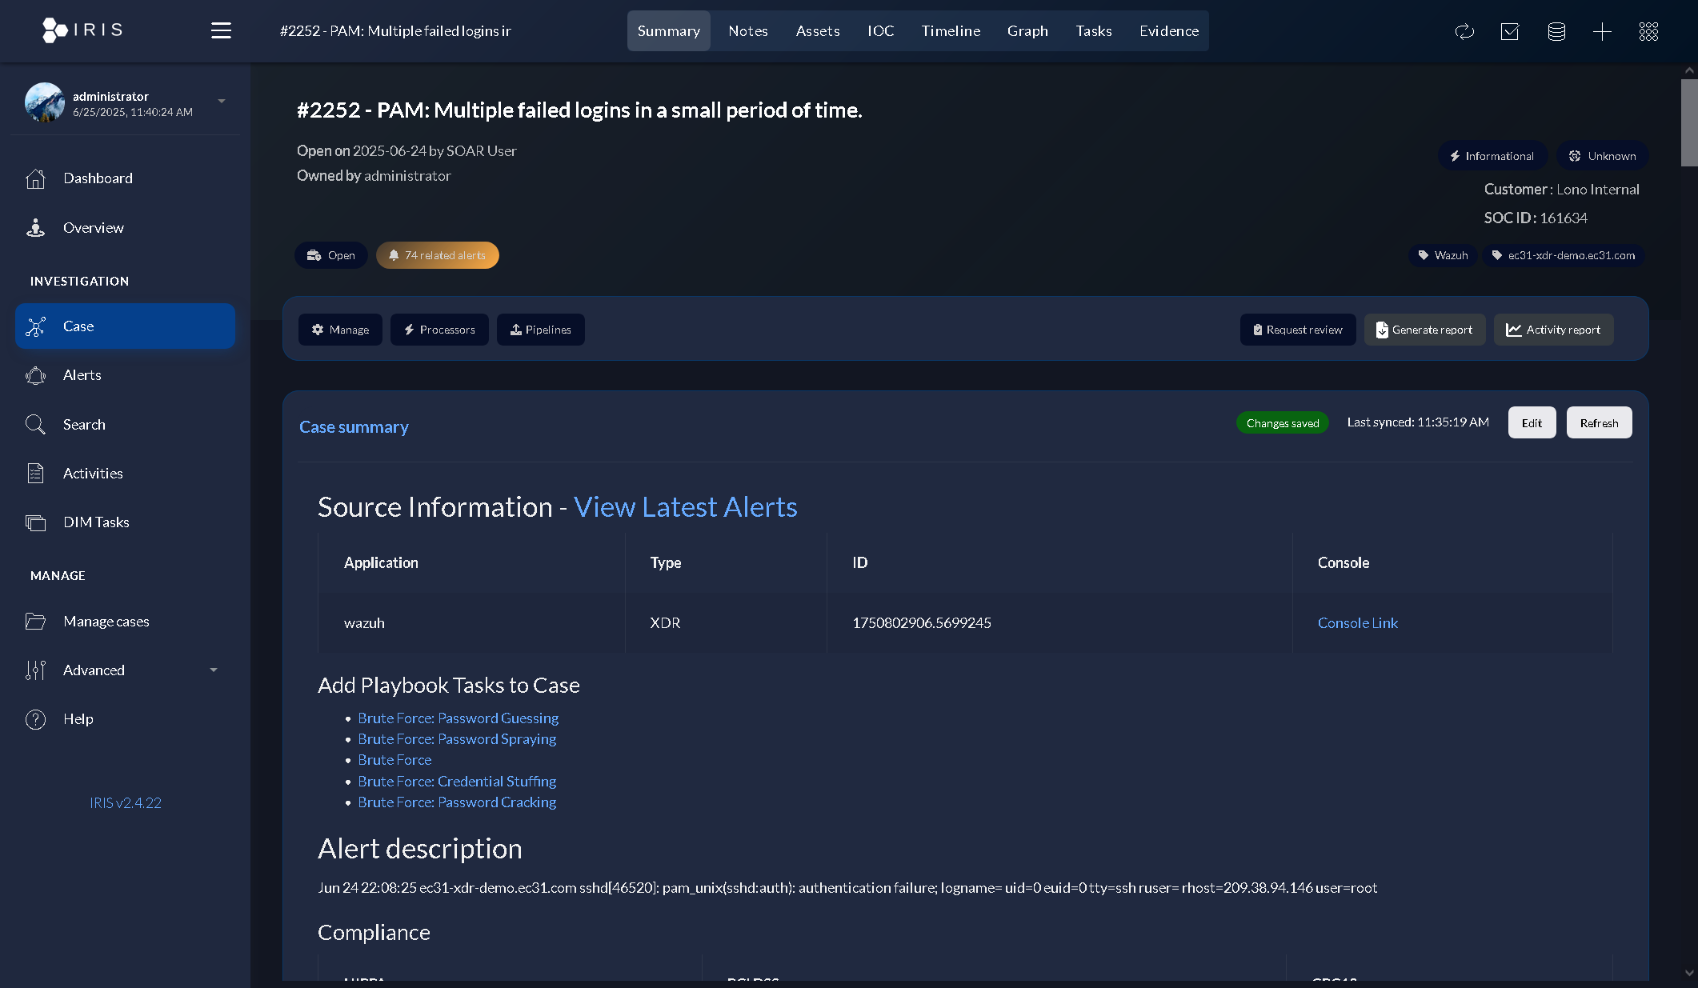
A case as it opens: 74 related alerts correlated onto one incident, playbook tasks already attached
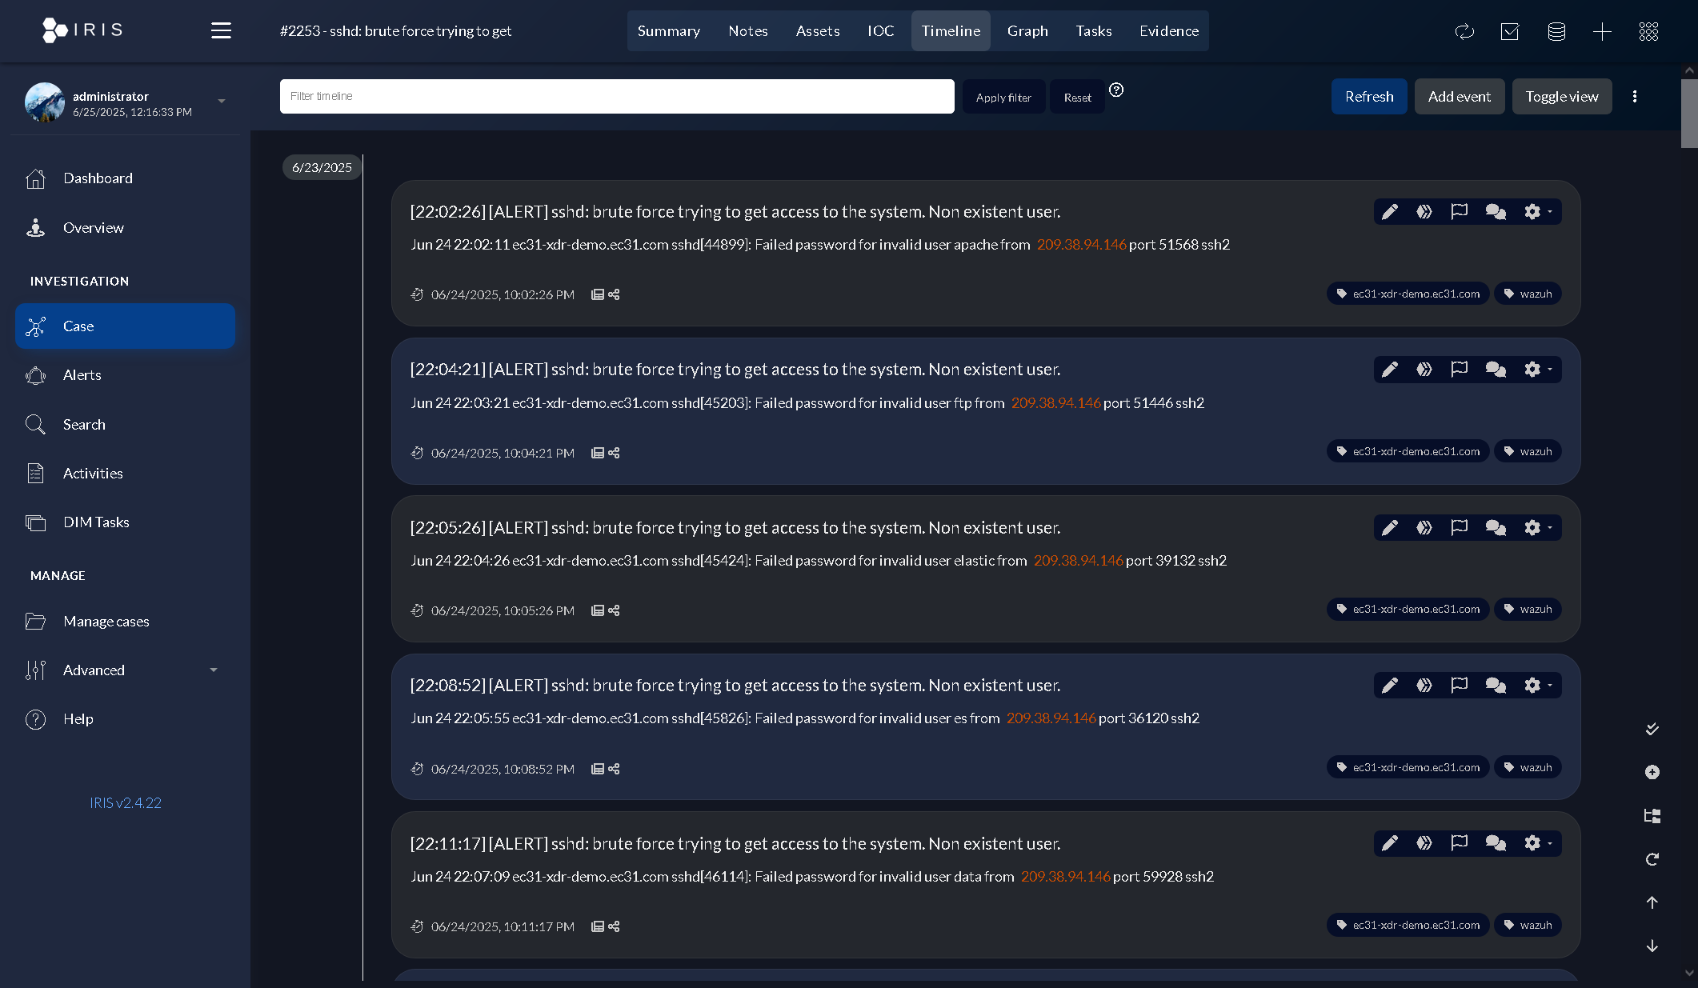
The alert timeline for that case: every failed login, source IP highlighted
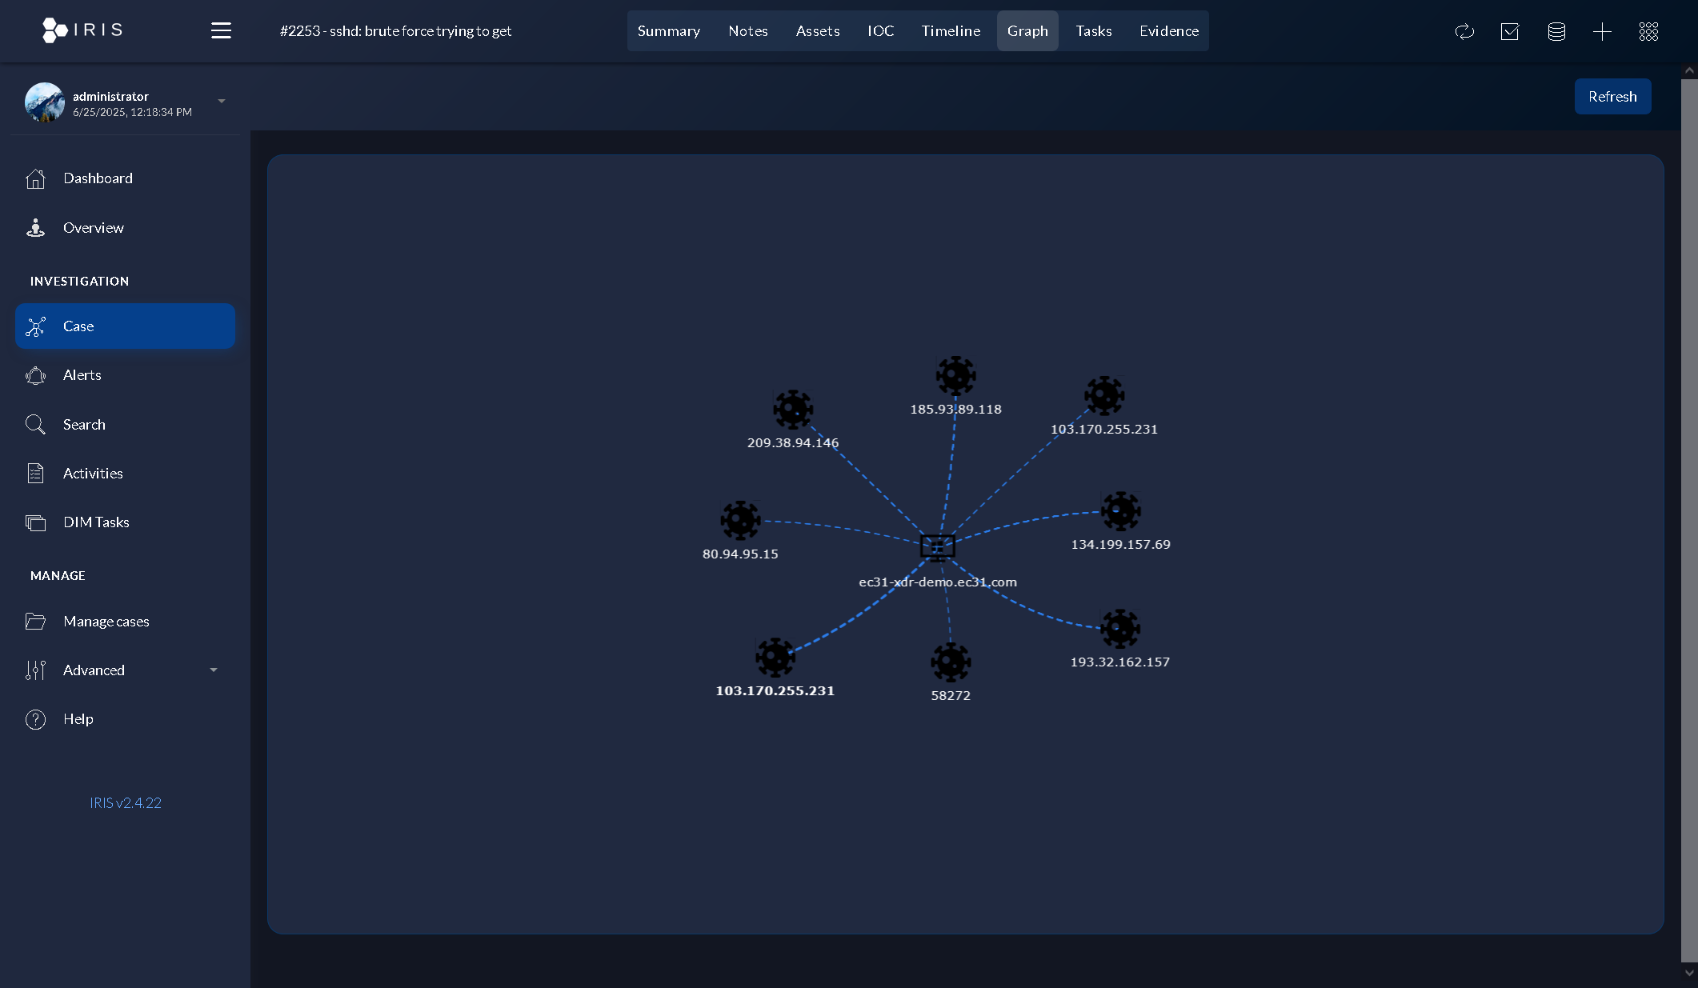
The IOC graph: one host against six attacker IPs
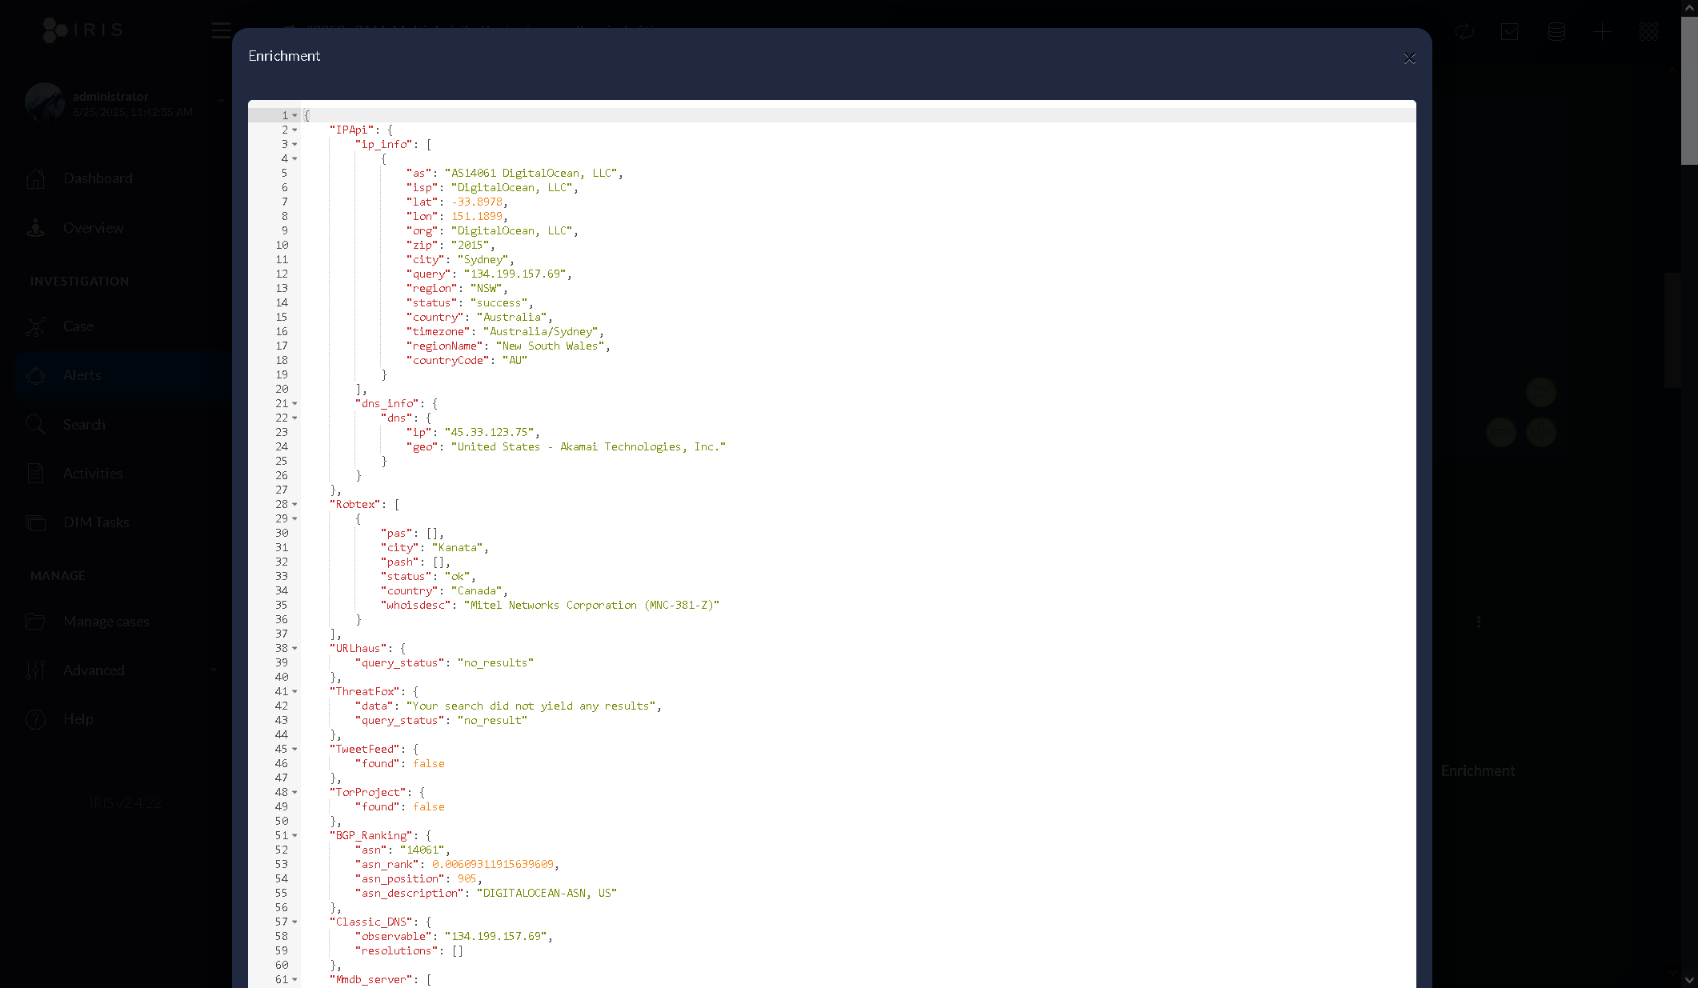
Enrichment on a single indicator: geolocation, ASN and BGP ranking, passive DNS, threat feeds, Tor exit checks

Under the hood

How it got built

The runbook library came first. Security teams do not need another dashboard, they need the steps, so a set of technique cards was built out, one per MITRE ATT&CK entry including sub-techniques, and a generator compiled them into runbooks with real procedure: what to look at, how to contain it, when to escalate. 656 of them, every one written out. Then the plumbing: orchestration workflows for ingestion, enrichment and remediation, an enrichment layer with a dozen analyzers behind it, and case management to hold the investigation. The assembly is the product, and that is what makes the business model work. Because the platform is streamlined and the pieces are pre-built, Lono can do the development work for the customer and still run the whole thing on a flat monthly rate, live in two weeks instead of six months.

656
runbooks, MITRE-keyed
203
MITRE techniques
Flat
monthly, fully managed
2 wks
to production

Stack

SOAR XDR DFIR case management IOC enrichment MITRE ATT&CK Python Laravel 11 Livewire 3

Working on something like this?

One sentence about the problem is enough.

john@johnsabo.org